What Is the Zero Trust Security Model?
 09.24.2026

Zero Trust is a security approach based on the principle that a network or user should not be considered trustworthy simply because of their location or previous access history. In this article, we will examine what the Zero Trust model is, how it works, its core principles, and its areas of use.
What is Zero Trust?
Zero Trust is a security approach that adopts the principle of “never trust by default, verify every access request” instead of “trust but verify.” Even if a user, device, or application has been previously authenticated, access requests are evaluated according to security policies.
In traditional security models, an organization's internal network may be considered more trustworthy, while external networks are viewed as more risky. In the Zero Trust approach, being inside or outside the network is not, by itself, an indicator of trust.
How does Zero Trust work?
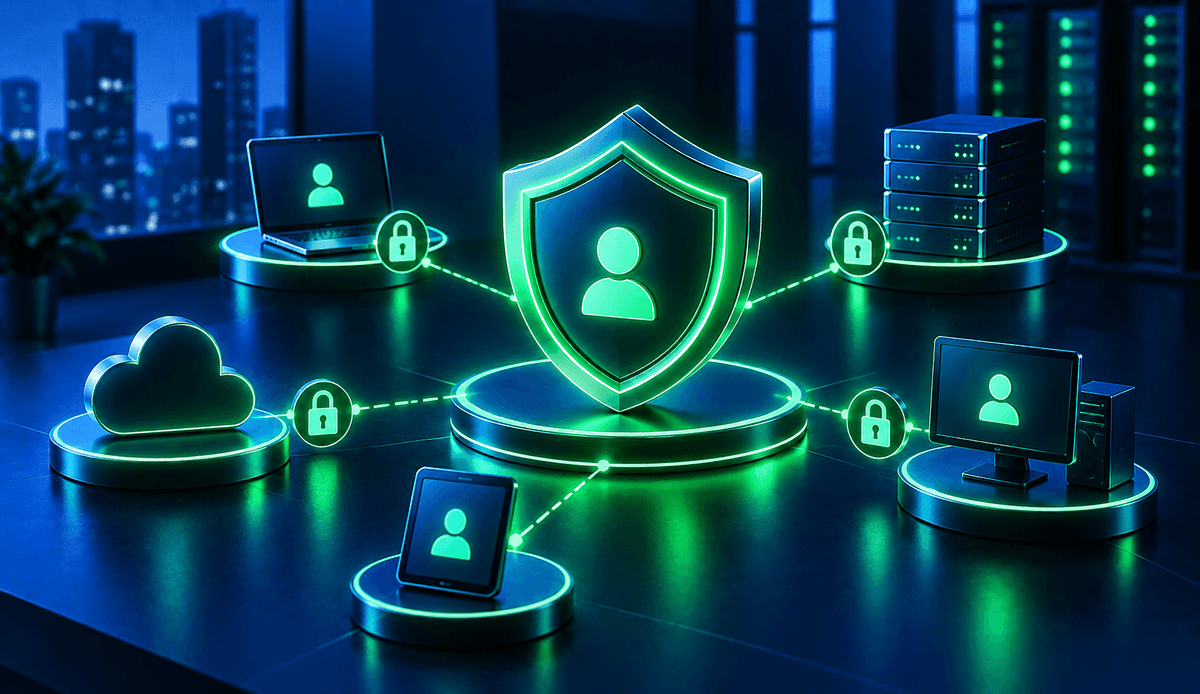
In the Zero Trust model, access is not treated as a one-time process. The user's identity, the security status of the device, the resource they want to access, and the applicable security policies are evaluated together when making an access decision.
In this approach, it is important not to grant users or devices more privileges than necessary. This can help limit an attacker's access to other systems if an account or device is compromised.
What are the core principles of the Zero Trust security model?
Zero Trust is built around a set of security principles. These principles cover different layers of security, from controlling access to continuously evaluating users and devices.
Why is every access request verified?
The fact that a user has been authenticated previously does not mean that all subsequent access requests are automatically secure. In the Zero Trust model, access requests are re-evaluated based on predefined conditions.
Authentication and authorization processes can be considered together with information such as the resource the user wants to access. This allows access decisions to be made in a more controlled manner.
What is the principle of least privilege?
The principle of least privilege means that users or systems should only have the level of access they need to the resources required for their tasks. Granting users broad permissions that are not necessary for their responsibilities is avoided.
This approach can help limit the potential scope of access if an account is compromised.
For example:
- An employee may only access the applications required to perform their job.
- An application may only access the system resources it needs to operate.
- Temporary access can be restricted to a specific period.
Why are user and device security evaluated together?
Zero Trust is not limited to verifying a user's identity. The security status of the device being used can also be evaluated during access.
Access from devices that are outdated, do not comply with security policies, or have not passed required security checks can be restricted. This means that having a secure user account alone is not considered sufficient.
Why is network traffic monitored?
Monitoring access and activity within systems plays an important role in the Zero Trust approach. Detecting unusual behavior can help security teams investigate potential threats at an earlier stage.
For this reason, access logs, security events, and system activities can be monitored in accordance with appropriate policies.
What is the difference between Zero Trust and the traditional security model?
In traditional approaches, users within an organization's network may be assumed to be more trustworthy. Zero Trust, on the other hand, does not automatically consider a request coming from inside the network to be trusted.
The fundamental difference is that trust is established based on verification and access policies rather than network location. For this reason, Zero Trust can be suitable for evaluating different access scenarios in environments where remote work and cloud services are widely used.
| Traditional Approach | Zero Trust Approach |
|---|---|
| Network location may play an important role in trust decisions. | Network location is not, by itself, an indicator of trust. |
| Access from the internal network may be considered more trustworthy. | Every access request is verified. |
| Broad access permissions may be granted. | The principle of least privilege is applied. |
| Security may focus on protecting the network perimeter. | Users, devices, applications, and resources are evaluated together. |
What technologies does Zero Trust use?
Zero Trust is not a single product or technology. It is a security approach that combines different security technologies.
Identity and access management, multi-factor authentication, device security, and network access controls can all be part of a Zero Trust architecture.
Depending on the systems being used, technologies such as the following may be utilized:
- Identity and Access Management (IAM): Manages user identities and access permissions.
- Multi-Factor Authentication (MFA): Uses an additional verification method alongside a password.
- Device security: Helps assess the security status of corporate devices.
- Network access controls: Determines which resources users and devices can access.
- Security monitoring systems: Helps track access and unusual activities.
Where is Zero Trust used?
Zero Trust can be applied across different organizations and technology environments. It can be particularly useful in environments where users access corporate resources from different locations, devices, and applications.
Cloud services, remote work systems, enterprise applications, and hybrid IT infrastructures are among the areas where the Zero Trust approach can be considered.
What are the advantages of the Zero Trust model?
Zero Trust helps move security controls beyond the network perimeter and enables access policies to be established based on users, devices, and resources.
Some of the benefits this approach can provide include:
- Helps limit unnecessary access privileges.
- Supports controlling the scope of access available to a compromised account.
- Enables the security status of users and devices to be evaluated together.
- Helps create more controlled policies for access from different locations.
- Supports monitoring access activity and investigating security incidents.
What should be considered when implementing Zero Trust?
Implementing Zero Trust does not simply mean purchasing a new security product. Organizations need to understand their existing users, devices, applications, data, and access requirements.
Defining access policies correctly is also important. Policies that are too restrictive may disrupt employees' workflows, while overly broad permissions can weaken one of the core objectives of Zero Trust: limiting access.
For this reason, the implementation process should include analyzing the existing infrastructure, identifying access requirements, and regularly reviewing security policies.
Zero Trust extends the security approach beyond network boundaries by focusing on verifying every access request and granting only the necessary level of access in a controlled manner. Evaluating identities, devices, applications, and access policies together can help create a more controlled security environment in modern IT infrastructures.